
MiCA compliance
MiCA compliance is the work a crypto firm does to meet the Markets in Crypto-Assets Regulation (EU) 2023/1114, which has applied in full across the European Union since 30 December 2024. The rules reach crypto-asset service providers, issuers of stablecoins and every firm that offers other crypto-assets to the public or seeks their admission to trading.
For a service provider, compliance starts with an authorization from a national supervisor and continues every day after it, with duties on capital, governance, client assets, complaints and conflicts of interest. An issuer publishes and updates a crypto-asset white paper, and a stablecoin issuer also manages a reserve of assets and honors the redemption right of its holders.
Who has to comply with MiCA
MiCA sorts crypto-assets into three groups and attaches its own duties to each of them. Issuers of asset-referenced tokens need an authorization under Article 16, issuers of e-money tokens must be a credit institution or an electronic money institution under Article 48, and an offeror of any other crypto-asset notifies and publishes a MiCA white paper.
Crypto-asset service providers form the largest group of firms under MiCA. A crypto exchange, broker or custodian needs a CASP license under Article 59, while banks, investment firms and other financial entities can notify their supervisor under Article 60 instead. ESMA keeps an interim register of both groups, and Germany has the most entries, more than 100 of them notifications by banks and other financial entities to BaFin.
What a CASP keeps in place after authorization
Authorization is the start of supervision, and Articles 66 to 74 of MiCA set the duties that apply to every CASP from then on. A CASP acts honestly, fairly and professionally in the best interest of its clients, holds prudential safeguards under Article 67, keeps a management body of good repute, segregates client crypto-assets and funds, handles complaints and conflicts of interest under written procedures, controls its outsourcing and keeps a plan for an orderly wind-down. Each service adds rules of its own, for example a custody policy and a register of client positions for custody under Article 75, or operating rules and market surveillance for a trading platform under Article 76.
The Commission has filled in many of these duties with delegated regulations, which ESMA lists in its overview of Level 2 and Level 3 measures. Delegated Regulation (EU) 2025/299 sets the measures for continuity and regularity of services, 2025/294 the complaints procedure, 2025/1142 the conflicts of interest rules and 2025/1140 the records a CASP keeps on its services, orders and transactions.
Rules next to MiCA: travel rule, AML and DORA
Several duties that crypto firms handle under the heading of MiCA compliance come from other EU laws. The travel rule in the Transfer of Funds Regulation (EU) 2023/1113 requires CASPs to send and check originator and beneficiary data with every crypto transfer, without a minimum amount, and it applies from the same date as MiCA. Anti-money laundering duties come from national law today and from the EU AML Regulation from July 2027, and the rules on crypto AML set out what that means for transaction monitoring.
CASPs are also financial entities under the Digital Operational Resilience Act, which has applied since 17 January 2025. DORA asks for an ICT risk management framework, incident reports to the supervisor, resilience testing and a register of ICT third-party providers. Market abuse rules sit inside MiCA in Title VI: anyone who professionally arranges or executes crypto transactions must detect and report suspicious orders, the core of the rules on crypto market abuse.
Finance Loop and MiCA compliance
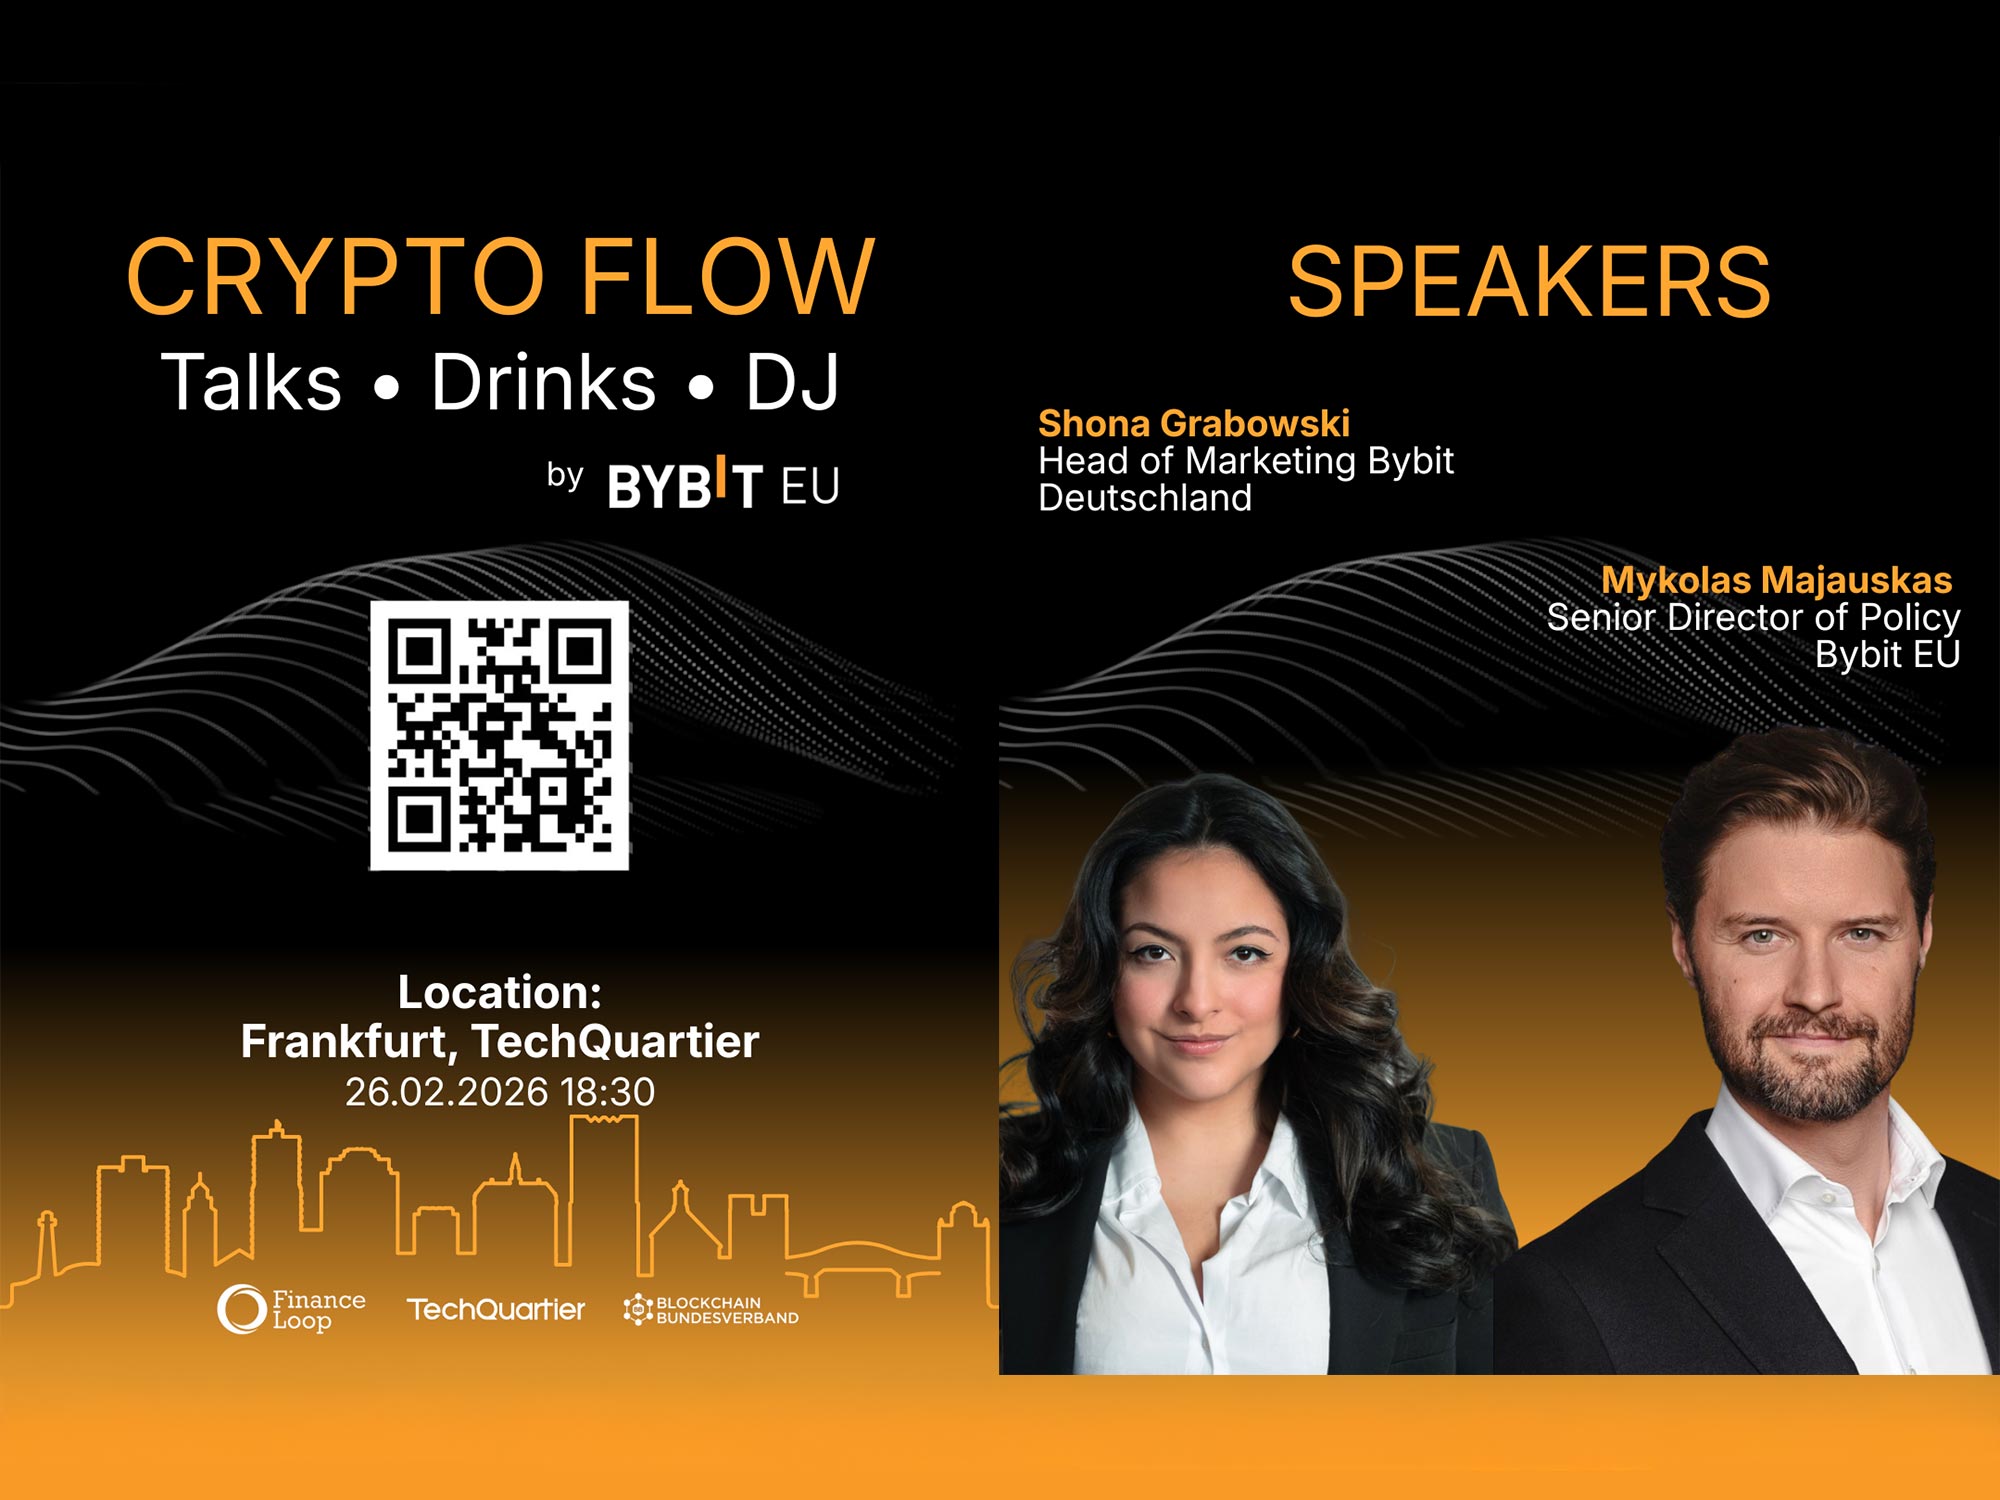
Compliance under MiCAR was one of the subjects of the Bybit EU Crypto Evening, an evening of talks at TechQuartier in Frankfurt with Finance Loop as a partner. Mykolas Majauskas, Senior Director of Policy at Bybit EU, spoke there about market positioning and compliance under the regulation. For teams that want structured training, EBS Executive School and the law firm HEUKING teach a German-language MiCAR certificate program.
Upcoming events on crypto regulation
What MiCA compliance means
MiCA compliance means that a crypto firm holds the authorization or notification its activity in the EU requires and meets the conduct, capital, governance and disclosure rules of Regulation (EU) 2023/1114 on every day it operates. Article 111 lets national supervisors fine a company at least up to 5 million euros or 5 percent of annual turnover for breaches of the CASP rules, and up to 15 million euros or 15 percent for market manipulation. ESMA also asked supervisors to act against providers that kept serving EU clients without a license after the MiCA transitional period.
MiCA compliance for banks
A bank that offers crypto services under Article 60 notifies its supervisor at least 40 working days before it starts and does not need a separate CASP license. It is exempt from the prudential safeguards of Article 67, which its banking capital rules already cover, but the conduct, custody, complaints and market abuse rules of MiCA apply to its crypto business in the same way as to a licensed CASP.
How to check whether an exchange is MiCA-compliant
The fastest check is the ESMA interim register of crypto-asset service providers, which names each authorized or notified firm with its home supervisor, the date, the services covered and the countries it passports into. The register can lag behind, so the list of the national supervisor, for example BaFin in Germany or the AMF in France, is the second place to look. Clients should also confirm that their contract is with the authorized EU company, because one group can run an EU firm and a firm outside the EU under the same brand.
A MiCA compliance checklist for CASPs
A CASP that reviews its MiCA compliance can start with the items its supervisor checked at authorization: the services it provides against the services authorized, own funds against Article 67 and Annex IV, the fit and proper file of the management body, the segregation of client crypto-assets and funds, the custody policy, the complaints and conflicts of interest procedures, outsourcing contracts and the wind-down plan. The list continues with market abuse surveillance under Article 92, the travel rule data flows, the DORA register of ICT providers and the ESMA guidelines that apply to its services, such as the guidelines on suitability for advice and portfolio management.
The compliance officer under MiCA
MiCA does not create a job title for a compliance officer, but Article 68 requires every CASP to adopt policies and procedures that are effective enough to ensure compliance with the regulation. Staff who give information or advice on crypto-assets must prove knowledge and competence under ESMA guidelines that apply from 28 July 2026, for information staff with a qualification of at least 80 hours plus six months of experience. The MiCAR certificate program of EBS Executive School is one way for compliance staff to document that knowledge.
MiCA compliance and Finance Loop
Finance Loop covers MiCA in its Risk & Compliance track, together with the travel rule, crypto AML and DORA. Finance Loop brings compliance officers of banks, brokers and crypto firms together with lawyers and supervisors at its events in Frankfurt, Munich, Berlin and Hamburg.
Finance Loop is a professional network and has the goal of driving the institutional use of emerging technologies in finance, such as AI, digital payments, cloud and blockchain solutions. Finance Loop helps its members build skills and personal networks in these fields: Investment & Digital Assets, Payments & Digital Money, Digital Infrastructure & Sovereignty, and Risk & Compliance.